17
Jan
Jan
Why Multifactor Authentication (MFA) is Essential for Digital Security
- Quick Heal / 2 years
- January 17, 2025
- 0

In times where cyber threats are becoming increasingly sophisticated and prevalent, relying solely on passwords for account security is no longer sufficient. Hackers employ various techniques, such as phishing, social engineering, and brute-force attacks, to compromise user credentials and gain unauthorized access to sensitive data. This is where multifactor authentication (MFA) comes into play as a crucial security measure.
This blog will delve into the importance of MFA, explain how it works, and guide you through the process of setting it up for your accounts.
Related read: How to Safeguard Your Passwords from Cracking Attacks
What is MFA (Multi-Factor Authentication)?
Multi-factor authentication (MFA) is a security system that requires users to provide two or more independent credentials to verify their identity before granting access to an account, application, or system. These credentials fall into three categories:
By combining factors from at least two of these categories, MFA creates a layered defense mechanism that significantly enhances account security. Even if an attacker manages to compromise one factor, such as your password, they would still need to provide the additional factor(s) to gain access, making it much more challenging to breach your account.
Multi-Factor Authentication Examples
MFA helps prevent unauthorised access by requiring an additional identity check beyond your password. Everyday examples include:
- Email accounts: A password followed by approval on your registered smartphone helps block attackers who have stolen your password but cannot approve the login.
- Online banking: A password combined with an OTP sent to your registered mobile number adds a verification step before access is granted. Never share this OTP with anyone.
- Work accounts: A password paired with a physical security key requires possession of that key. FIDO2 security keys also resist phishing by verifying the website requesting authentication.
Everyday example: If someone steals your email password and tries to sign in, MFA requires an additional verification step on your phone. Rejecting an unexpected approval request helps prevent unauthorised access.
Why is Multi-Factor Authentication Necessary?
In the past, passwords were considered sufficient for securing accounts. However, with the increasing frequency and sophistication of cyber attacks, relying solely on passwords is no longer enough. Here are some reasons why MFA authentication has become a necessity:
Password vulnerabilities
Weak, reused, or compromised passwords are common entry points for cybercriminals. MFA adds an extra layer of protection, mitigating the risks associated with password vulnerabilities.
Data protection
MFA plays a crucial role in safeguarding sensitive data, financial accounts, and personal information. By requiring additional verification factors, MFA ensures that only authorized individuals can access this information, reducing the risk of data breaches and identity theft.
Compliance requirements
Many industries, such as healthcare and finance, have strict regulatory requirements that mandate the use of MFA to protect sensitive data. Implementing MFA helps organizations meet these compliance standards and avoid costly penalties.
Reduces Risk of Phishing and Fraud
MFA helps prevent attackers from accessing accounts using passwords stolen through phishing. Without the additional verification factor, a stolen password alone is insufficient. Phishing-resistant methods, such as FIDO2 security keys and passkeys, offer stronger protection because they are tied to the legitimate website.
Enhances Overall Account Security
MFA reduces dependence on passwords and helps protect against attacks that exploit weak, reused or leaked credentials. Enabling it across email, banking and work accounts reduces the chances of a compromised password leading to unauthorised access.
Adds an Extra Layer of Identity Verification
MFA requires users to verify their identity using factors from at least two different categories, such as a password and a registered security key. This additional check makes account access more difficult for attackers, even when they know the password.
What are the Benefits of Multi-Factor Authentication?
Implementing MFA cyber security offers several key benefits:
Enhanced security: MFA provides a significant boost to account security by requiring multiple independent factors for authentication. This makes it much harder for attackers to gain unauthorized access, even if they possess a user’s password.
Reduced risk of data breaches: By preventing unauthorized access, MFA helps minimize the risk of data breaches. This is particularly important for organizations that handle sensitive customer data or intellectual property.
Improved user trust: Implementing MFA demonstrates a commitment to security and can help build user trust. When users know their accounts are protected by MFA, they are more likely to feel confident in using your services or entrusting you with their personal information.
Flexibility and convenience: Modern MFA solutions offer a range of authentication methods, allowing users to choose the factors that best suit their preferences and needs. Many MFA methods, such as push notifications or biometric authentication, provide a seamless and user-friendly experience.
How Does Multi-Factor Authentication Work?
The MFA authentication process typically involves the following steps:
User enters username and password: The user initiates the login process by entering their username and password, as they would in a traditional single-factor authentication system.
MFA prompt: After verifying the username and password, the system prompts the user to provide an additional authentication factor. This could be a one-time passcode (OTP) sent via SMS or email, a code generated by an authenticator app, a biometric scan, or a hardware token.
User provides additional factor: The user retrieves the additional factor and enters it into the system. For example, they might input the OTP received via SMS or provide a fingerprint scan.
Verification and access: The system verifies the additional factor provided by the user. If the factor is valid, the user is granted access to their account or the requested resource.
Related read: Smart Security: the Role of Machine Learning in Identifying Fraud
Multi-Factor Authentication vs. common security feature
Security threat | Basic security measures alone | Additional protection with MFA |
Stolen passwords | A scammer may log in using your password. | Requires another verification factor to gain access. |
Guessed security answers | Personal answers may be guessed or found online. | Adds verification beyond information a scammer may know. |
Unauthorised logins | Password-only login cannot distinguish you from someone using your credentials. | Requires a registered device, biometric or another independent factor. |
Phishing scams | Fake login pages can steal passwords. | Phishing-resistant MFA, such as FIDO2 security keys, helps block authentication on fake websites. |
Personal data theft | Compromised login details may expose private information. | Adds a barrier before attackers can access account data. |
What is Adaptive Multi-Factor Authentication?
Adaptive MFA is an advanced form of multi-factor authentication that dynamically adjusts the authentication requirements based on the user’s risk profile and context. It takes into account factors such as the user’s location, device, network, and behavior patterns to determine the appropriate level of authentication.
For example, if a user tries to access their account from a new device or an unfamiliar location, adaptive MFA might require a stronger form of authentication, such as a biometric scan or a hardware token. On the other hand, if the user is accessing their account from a trusted device and location, adaptive MFA might only require a simple push notification for approval.
Adaptive MFA provides a balance between security and user experience by applying the right level of authentication based on the risk level of each login attempt. This helps minimize friction for legitimate users while still maintaining a high level of security.
Related read: How to Protect Yourself from Fake OTP Scams
Types of Multi-Factor Authentication
SMS or Email OTP
A one-time passcode is sent to your registered mobile number or email address. When used alongside a password, it helps block scammers who know your password but cannot access the code. However, attackers can still steal OTPs through phishing or compromised accounts, so never share them.
Authenticator Apps
Authenticator apps generate short-lived codes on your smartphone. A scammer with only your password would also need a valid code to sign in, helping protect your personal information. These codes can still be phished, so enter them only on the legitimate service.
Biometric Authentication
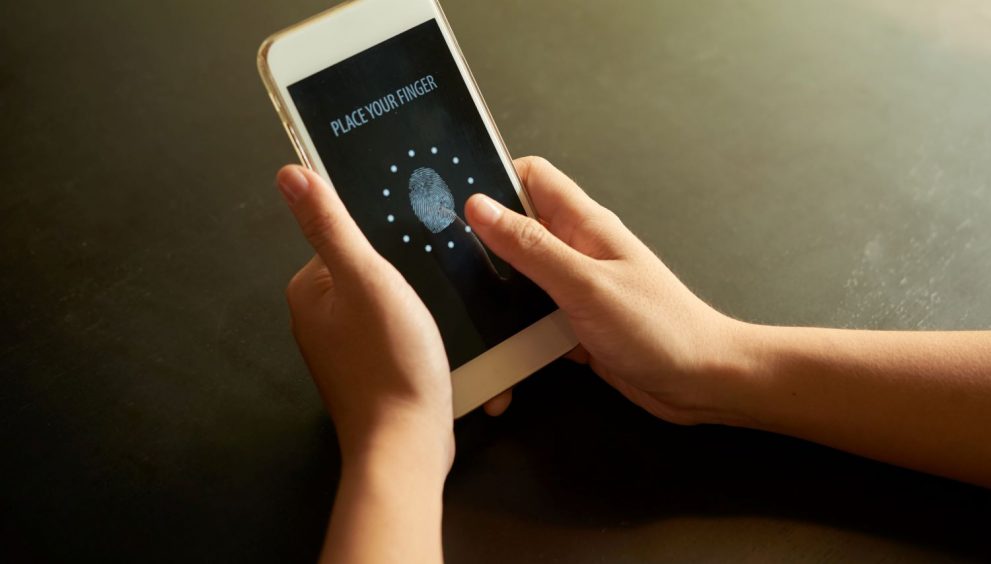
Fingerprint or facial recognition checks whether the person authenticating matches an enrolled biometric. For example, an unknown face should fail verification, helping prevent someone else from accessing protected accounts or data. Biometrics can form part of MFA when combined with another factor, such as a registered device.
Hardware Tokens
Physical security keys or OTP tokens require possession of a separate device. This helps prevent remote scammers from accessing your account with a stolen password alone. FIDO2 security keys also verify the website requesting authentication, helping block fake login pages.
Push Notifications
A notification on your registered device asks you to approve or deny a login attempt. This helps stop scammers who have your password but cannot approve the request. Reject unexpected prompts; number matching adds protection by requiring you to match the number shown during your own login.
Process for Multi-factor authentication setup
Setting up MFA for your accounts is a straightforward process. Here’s a general step-by-step guide:
Enable MFA: Look for the MFA or two-factor authentication (2FA) option in your account’s security settings. Enable this feature to start the setup process.
Choose your preferred MFA method: Select the MFA method that best suits your needs and preferences. Common options include SMS, authenticator apps, biometric authentication, and hardware tokens.
Configure the selected method: Follow the instructions provided by the platform to set up your chosen MFA method. This may involve registering your mobile number, scanning a QR code to set up an authenticator app, or configuring a hardware token.
Verify and test: After setting up MFA, verify that it is working correctly by logging out and logging back in. You should be prompted to provide the additional authentication factor.
When choosing an MFA method, consider factors such as security, convenience, and compatibility with your devices. It’s also a good idea to set up backup methods in case your primary method is unavailable (e.g. if you lose your phone with the authenticator app). For added security and convenience, consider using a comprehensive security solution like Quick Heal Total Security, which offers advanced features like MFA, malware protection, and secure browsing.
Use Multi-Factor Authentication for Added Security
Today, multifactor authentication (MFA) has become a critical component of a robust cybersecurity strategy. By requiring users to provide multiple independent factors for authentication, MFA significantly enhances account security and helps protect sensitive data from unauthorized access.
To stay ahead of evolving cyber threats, it is crucial to enable MFA for your most important accounts, such as email, social media, and online banking. By adopting MFA as part of your digital security practices, you can take a proactive step towards safeguarding your personal information and sensitive data from cybercriminals. Remember, cyber security MFA is not a one-time solution but an ongoing process. Stay informed about the latest security best practices, regularly update your software and devices, and remain vigilant against potential threats.